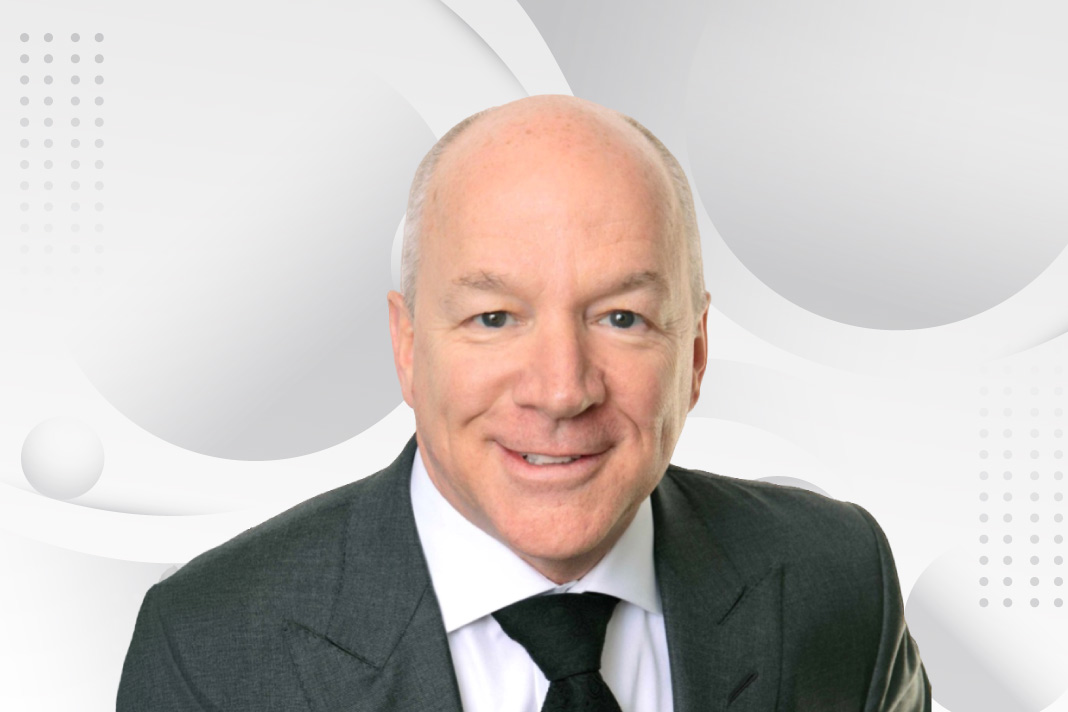
Companies can list every security tool they own and still stumble in the first hour of an attack. DXC’s Director of Cybersecurity says the fix is deciding, in advance, who acts and what keeps running.
Picture the first hour of a cyberattack. An alert fires. The security tools have done their job. And then, in too many companies, everyone looks at everyone else.
Who decides whether this is a real attack? Who has the authority to isolate a system? Which services must keep running while the team investigates? Most security leaders can list every tool they own. Fewer can say who makes those calls, or whether anyone has practiced making them under pressure.
That gap, not geography, is the widest Daniel Churches sees across the regions he covers. As director of cybersecurity for DXC Technology, he works with companies across Asia-Pacific, Japan, the Middle East and Africa, where economies, regulators and levels of maturity differ sharply. The pattern holds nearly everywhere: strong defenses on paper, thin plans for what comes after a breach.
In this interview, Churches takes on the questions security chiefs often avoid. Should a typical company fear criminals or nation-states more? Do data localization and breach-reporting rules make companies safer, or just busier with paperwork? Can outsourcing ever transfer accountability? His answers keep returning to one blunt piece of advice: plan for the breach, not just for preventing one.
Full interview;
You cover regions with very different economies and regulators. Where is the widest gap between how ready companies think they are and how ready they actually are?
The widest gap I see is not geographic. It is between having security tools and being ready to manage a breach.
Most security leaders can tell you what they have deployed – endpoints, firewalls, maybe SIEM. However, the more revealing conversation starts when you ask what happens after an alert comes in. Who decides whether it is a real attack? Who has the authority to isolate an affected system? Which services must keep running while the team investigates? And has anyone put those decisions into practice under pressure?
That is where a strong defensive stack can give a false sense of readiness. If the tools generate alerts, but the team cannot quickly make sense of them, contain an attack, and restore normal operations, the business remains exposed. I encourage clients to test the whole journey through an incident, including how they will keep working while recovery is underway.
Also Read: Your Oldest Legacy System Is How You Grant Admin Rights
Digital growth in emerging markets is outpacing security. Is that a ticking time bomb, or an advantage because defenses are built from scratch?
That may have been a fair description of some markets a few years ago. Today, though, I am seeing greater maturity, with organizations investing in security alongside their wider digital programs.
The real ticking time bomb is treating cybersecurity purely as a defensive expense. If you buy another point solution each time a new risk appears, without asking what the business needs to do next, you are likely adding cost and complexity without building much confidence in its ability to operate and grow.
Security has a broader role. It gives businesses the confidence to adopt AI, connect new services, and use data in new ways, knowing they can manage the risks and withstand disruption. This is where emerging markets have an advantage: they can build new digital capabilities at speed while designing resilience in from the outset.
Nation-state hackers get the headlines, but criminals hit most victims. Which should a typical company fear more?
For most companies, criminal activity is the more immediate operational concern. Ransomware, fraud and extortion can interrupt everyday services, affect customers and erode trust. The question is whether the organization can spot an attack, limit its spread and continue operating.
While most national governments have established security protocols to monitor and assess nation-state threats, this does not mean those threats can be ignored, particularly in critical infrastructure and strategic sectors. Priorities should reflect the organisation’s exposure, rather than which attacker gets the most headlines.
In either case, I would ask the same practical questions: which services matter most, where an attacker could gain access, and how quickly you could contain an incident and recover?
Also Read: Ford Gave Us The Five-Day Workweek. AI Should Make It Four
Governments across your markets are pushing data localization and tougher breach-reporting rules. Are companies safer, or is this a compliance paperwork industry?
You cannot rely on every organization to set the same standard for itself. Maturity varies considerably, so regulation has an important role in establishing baseline expectations and driving change across an industry.
The danger is the widening gap between meeting a compliance requirement and being secure in practice. A company might know where its data must be stored and meet a reporting deadline, yet still struggle to identify all the systems that hold sensitive information or to coordinate its response to a breach. Those rules matter, but completing the paperwork is not the outcome we should be chasing.
The better question is whether compliance work helps the organization understand its risks, improve its controls, and recover more effectively when something goes wrong. Done well, it strengthens resilience while making ongoing compliance easier to manage. If it only produces another set of forms, we have missed the point.
Many companies hand security to outside providers such as DXC. Can you outsource accountability, or does the blame always land back on the client’s desk?
If the first question during an incident is “Who do we blame?”, the organization is already losing valuable time. The harsh reality is that cybersecurity incidents will happen. What matters in that moment is how the company and its provider work together to limit the impact.
That starts with a shared understanding of risk and clearly defined responsibilities. Both parties need to know who monitors for threats, who can authorize containment, when an issue must be escalated, and how they will communicate and recover. Those procedures need to work in practice, not just exist in a contract.
When that groundwork is in place, people can get straight to the decisions that matter. Without it, they can spend the critical early hours debating responsibility while an attack spreads. Clear accountability allows the company and its provider to move beyond a defense-only mindset, enabling them to act together to contain a breach, minimize disruption, and restore operations.
Also Read: Inside Fal.Con 2026: CrowdStrike’s Bet on Securing AI
What is the one piece of advice you give every client that they almost never follow?
Plan for the breach, not just for preventing one.
Most organizations have spent time deciding how to keep attackers out. Fewer have worked through what they will do if an attacker gets in: which systems they would isolate, which services must stay available, who makes those calls, and what it will take to return to normal.
Run through that scenario with the people who would actually have to respond to a breach. You will learn much more about your readiness from that conversation than from another inventory of security tools.