Most breaches now begin with a valid login, not malware, and the fix starts with limiting what an identity can do after it signs in.
For years, the picture of a cyberattack was a hacker in a hoodie forcing a way through the firewall. Today, the more common entry is far less dramatic: Someone logs in with a stolen key.
Credentials taken from earlier breaches, hijacked sessions, abused tokens, and a well-timed request to approve a login prompt can all open the door. Once inside, an account with too much access can turn a single compromised identity into a full-scale breach. And the list of identities to protect keeps growing, including employees, service accounts, bots, and AI agents.
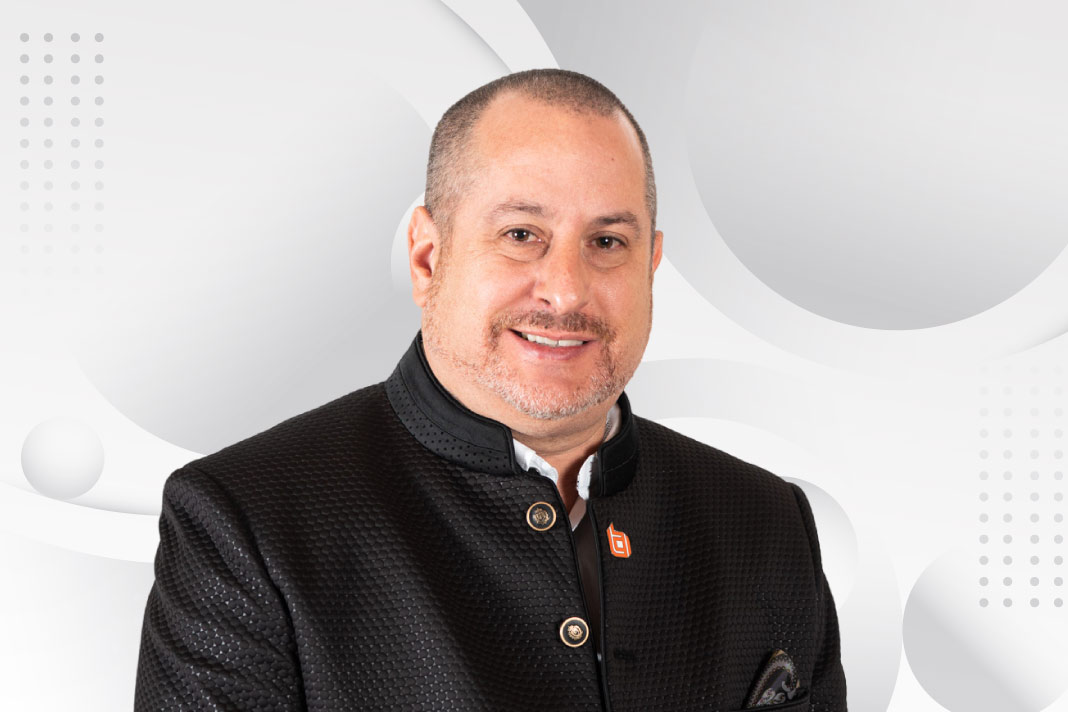
Few people have tracked that shift as long as Morey Haber, Chief Security Advisor at BeyondTrust, an identity and access security company. Haber has spent more than two decades in the IT industry and has written several books on attack vectors.
In this interview, he explains why identity is the new perimeter, how “privilege debt” quietly piles up, who is watching machine accounts, and where to start when the budget is zero.
Full interview;
Stolen credentials are among the most common ways to gain access to a network. Are attackers still “hacking in,” or are they just logging in?
Increasingly, they are logging in because it is currently the path of least resistance for breaching an organization. The stereotypical image of a threat actor launching malware to break through an application is becoming less representative of how many incidents begin. Why exploit a complicated vulnerability when you can steal credentials, hijack a session, compromise a token, abuse OAuth, or convince someone to approve an MFA request?
These attack vectors are the primary reasons that identity is the new perimeter. The network perimeter did not simply disappear; rather, it reorganized. It now surrounds every human, machine, application, workload, and AI agent with access to something valuable. If a threat actor authenticates using valid credentials and behaves sufficiently like the legitimate user, many traditional security controls will not detect the intrusion. Access was not compromised. Someone (or something) just logged in carrying a stolen key.
You have one hour and a typical company as your target. Where do you start, and why does it probably work?
I would start with the dark web and social media identity exposure, because that is where a threat actor can often find the shortest path between the outside world and internal privileged access. Public information can reveal employees, contractors, technology platforms, email conventions, cloud services, help-desk processes, and organizational relationships. Add credentials from previous breaches, phishing, infostealer malware, token theft, and social engineering, and suddenly the objective is not necessarily to exploit any known vulnerabilities or zero days. It is to find an identity that the organization already trusts and find a path to privileged access to compromise the environment.
Also Read: Ford Gave Us The Five-Day Workweek. AI Should Make It Four
What is the most reckless access setup you have seen at a major company?
One pattern I have encountered repeatedly is that everyone has administrator credentials, in some form, to perform the privileged tasks they need. This is usually well-intended, whether it be to change a setting, install new software, or install a driver for something as simple as a new printer.
In one environment I worked with recently, privileged access had accumulated across users and systems for years because removing it was considered an operational risk to normal operations. The irony was extraordinary, and the organization accepted a massive cybersecurity risk because it feared that applying least privilege might inconvenience someone or break something that had been working reliably for years.
That is how privileged debt turns into a cybersecurity risk. As with technical debt, nobody intends to accumulate it, but eventually the interest becomes painful when it’s stress-tested. Excessive privilege transforms a compromised identity from an incident into a potential breach, especially if the identity can be easily compromised or accessed via lateral movement.
Passwords have been declared dead for two decades, and we still use them. Who is to blame: users, vendors, or an industry that keeps promising a passwordless future?
Everyone gets a little credit for the claim, but no one wants to take responsibility for the solution, technically or even architecturally. Truthfully, users want convenience; vendors have historically designed applications around passwords for application and data security; and organizations maintain legacy systems that cannot easily support modern identity authentication and governance.
Once the industry announced the death of passwords, applications never evolved beyond requiring extreme complexity. Sure, we have SSO, OAuth, and EntraID integrations, but they just mask the password, even if biometrics is used for initial authentication. Passwordless authentication is absolutely a work in progress, but eliminating passwords does not eliminate identity attacks. It just makes them a little harder, and threat actors are adapting. They target sessions, tokens, recovery processes, help desks, authentication workflows, and the humans operating them via social engineering, MFA fatigue, man-in-the-middle attacks, etc.
The objective should not simply be “passwordless” for user convenience, but rather continuous verification for identity security to determine when access, behavior, and usage are inappropriate. These are all basic tenets of zero trust and can be applied to ensure even true passwordless installations have not been compromised.
Also Read: What Are VLA Models? How Vision, Language and Action Work
Machine and AI-agent accounts reportedly outnumber human ones. Who is watching them?
Often, there are not enough people simply because of the dynamic nature of non-human identities (NHIs) and the complexity involved in gaining accurate, up-to-date visibility into their operations. Organizations have spent decades building identity governance around humans: joiner, mover, and leaver processes.
Machines do not follow that lifecycle neatly, and AI makes the issue exponentially more complex. Service accounts, API keys, automation identities, bots, and now AI agents, can persist indefinitely or be created and destroyed dynamically at machine speed. Auditing and documenting these activities make ownership more than just a departmental task; it’s a full-fledged business imperative that requires the involvement of multiple stakeholders to achieve. This is because NHIs and AI may no longer be owned exclusively by IT, and, depending on purchasing and implementation, legacy teams may not even have visibility into the extent of their operations and deployments.
Today, in every organization, every non-human identity should have an owner, purpose, defined privileges, lifecycle, monitoring, and a mechanism for immediate revocation. If you cannot answer: “who owns this identity, why it exists, what it can access, and how we kill it”, you have an identity security problem.
In my experience, this is why most organizations cannot accurately report the ratio of human to nonhuman identities and why visibility and ownership are lacking.
Zero trust is on every vendor slide. Is it a real strategy or a buzzword, and what should a company with no budget do first?
Zero trust is absolutely a legitimate security model that marketing has turned into a marketing tagline. Its fundamental security controls remain sound — “do not grant trust merely because something successfully authenticated or happens inside a trusted network”.
For an organization with almost no additional budget, start with inventory and privilege access management. Determine who has administrative access, remove privileges that are unnecessary, disable stale accounts, identify shared credentials, enforce MFA where possible, review service accounts, monitor behavior, and understand where privileged pathways exist to prevent lateral movement.
As a strategy, zero trust does not begin with buying something. It is not a product, and that is why marketing solutions for zero trust are dangerous.
For organizations, embrace “Never trust, always verify”: begin by questioning established assumptions of normal operations, and conclude by asking questions based on appropriate behavior.
Also Read: Before You Audit Your Algorithms, Audit Your Data
What is the worst password habit you still see among senior executives?
The worst habit anywhere, and not just with senior executives, is password reuse. However, executives are particularly attractive targets because their identities frequently have access to sensitive communications, financial information, strategic systems, and the like, and their identities are known to the public.
A reused password is like leaving your house key under the doormat, and all someone needs to do is look before gaining unsanctioned access. Every password should be unique for every application and resource, whenever feasible. This is especially true for executives, since their authority can sometimes bypass normal processes, and attack vectors like deepfakes have been known to exploit this via social engineering. If you add a reused password to the mix, then they become an easy target for threat actors attempting to compromise their likeness and authority.
Should employees ever keep admin rights on their own laptops?
As a standing privilege, generally no. There are currently no legitimate situations where users, including developers and specialized administrators, need elevated access. However, occasionally needing administrative privileges to perform a task does not mean someone should operate as an administrator continuously or have access to standing privileges.
The better model for end users that might need administrative rights on their laptops is “just-in-time privileges. This technique provides elevation for the specific application, command, or task, for the minimum necessary period, and then access is terminated. The privileges should be ephemeral rather than permanent.
Therefore, the question operational teams should be asking is “What specifically requires privilege, for how long, and under what conditions?” in lieu of “Which user is requesting privileges?” This difference ensures no one should ever have administrative access on their work devices and eliminates the risk of standing privileges.
Also Read: The New Boardroom Problem: How Do You Measure AI’s ROI?
What security habit do you follow that makes your colleagues roll their eyes?
I question privileges relentlessly. When an application asks for administrator rights, access to contacts, location, files, a microphone, or my camera, my instinct is not to click “Allow”. My instinct is to ask “why?” and almost always I answer “Deny”!
This reaction probably stems from spending too many years looking at breaches in which the most damaging question was not “how did the threat actor get in?” but rather “why did the compromised identity have access to all of these resources in the first place?”
That is ultimately the lesson behind “identity is the new perimeter”. We cannot prevent every credential from being stolen, every token from being attacked, or every user from making a mistake. But we can control what an authenticated identity is allowed to do. In modern cybersecurity, authentication is not proof of trust. It is merely the beginning of the conversation, and denying access to resources can limit the blast radius when an identity is compromised. This is especially true when the blast radius can include our mobile devices and the laptop that we travel with every day.